ProductRanking is earned · anything paid is labeled
Fuzzlane
Fuzz your public API from your OpenAPI spec in CI. Finds the 500s before your users do.
RIRajesh IyerCONTRIBUTOR@raj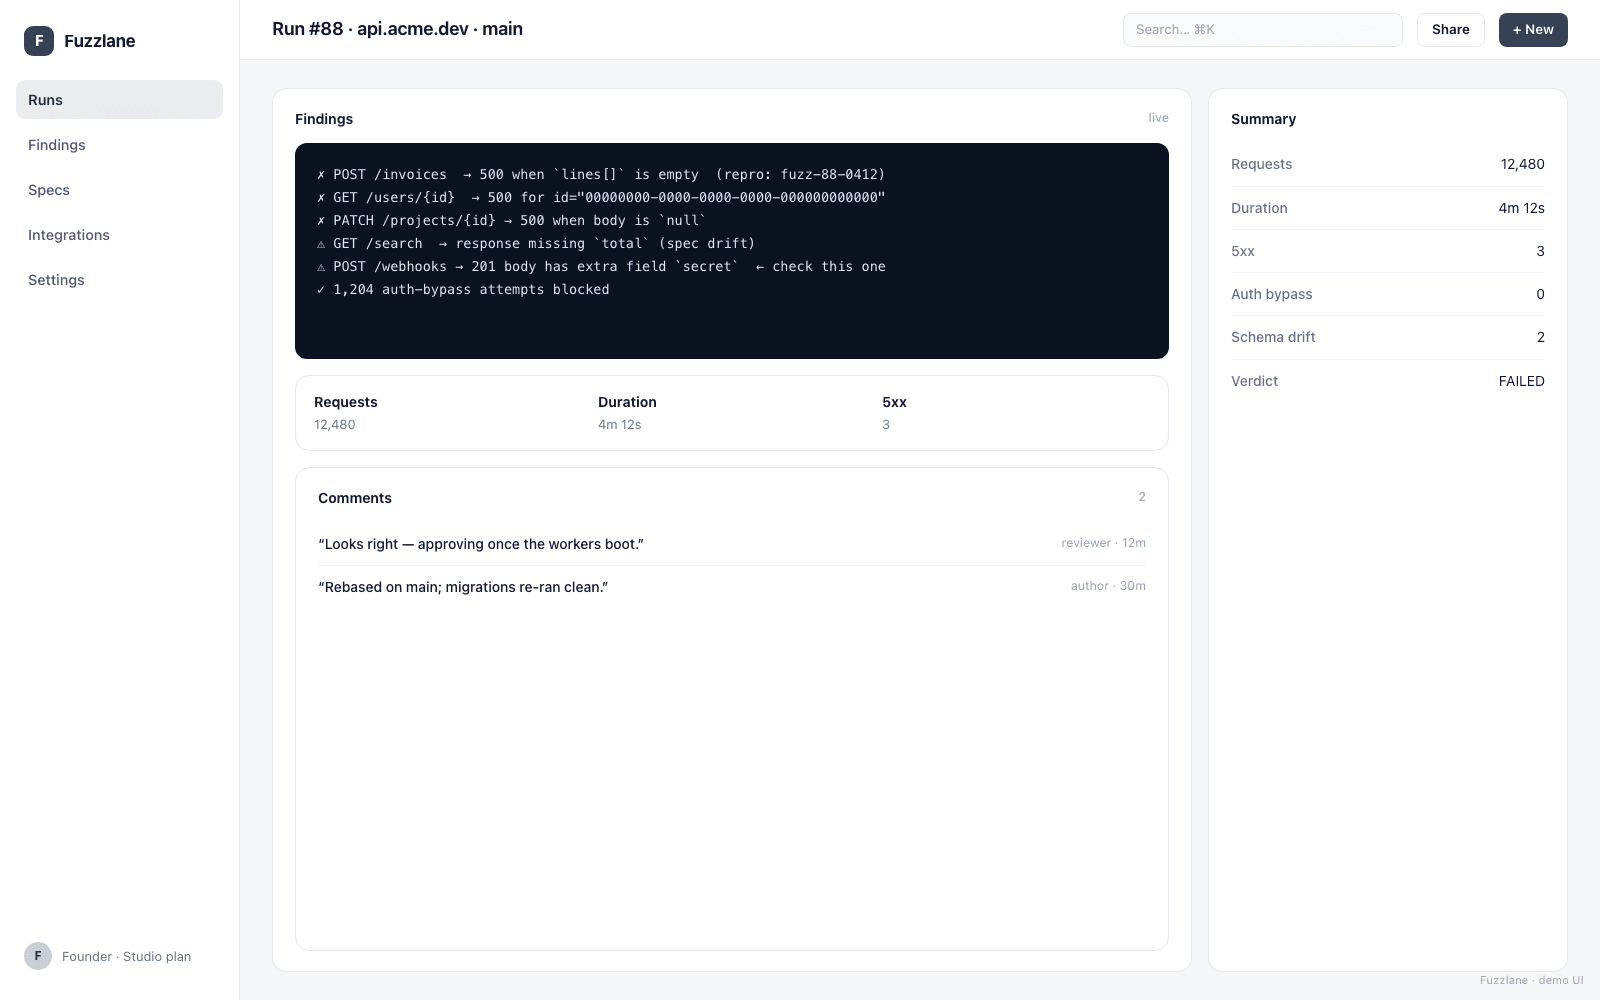
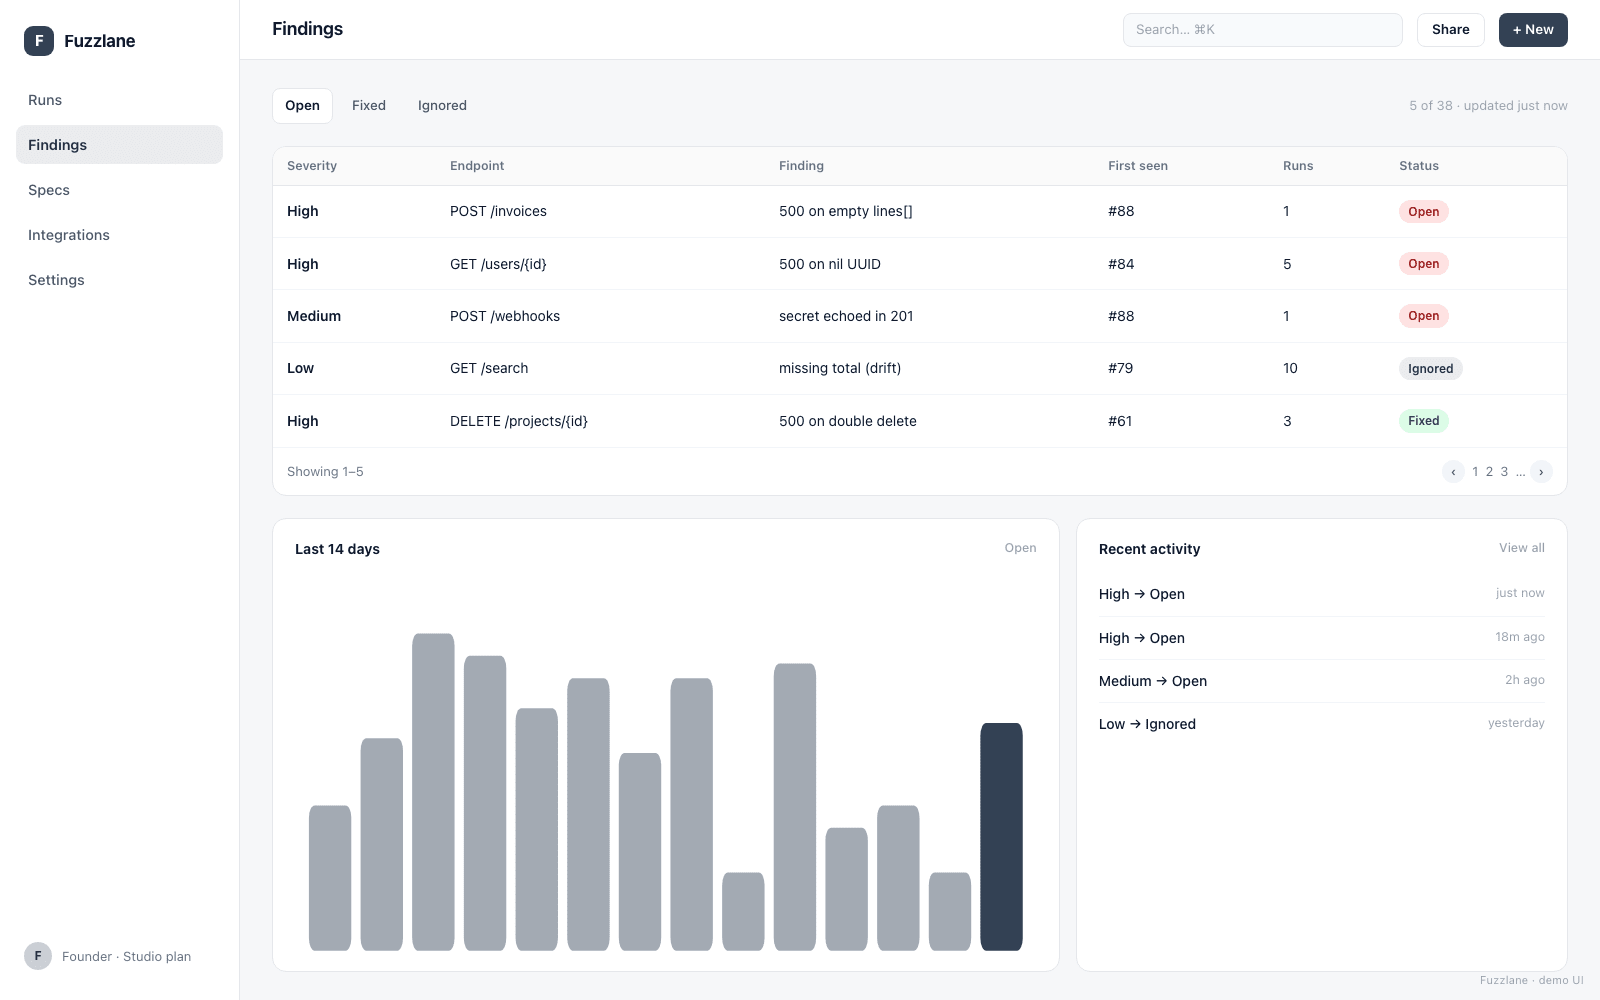
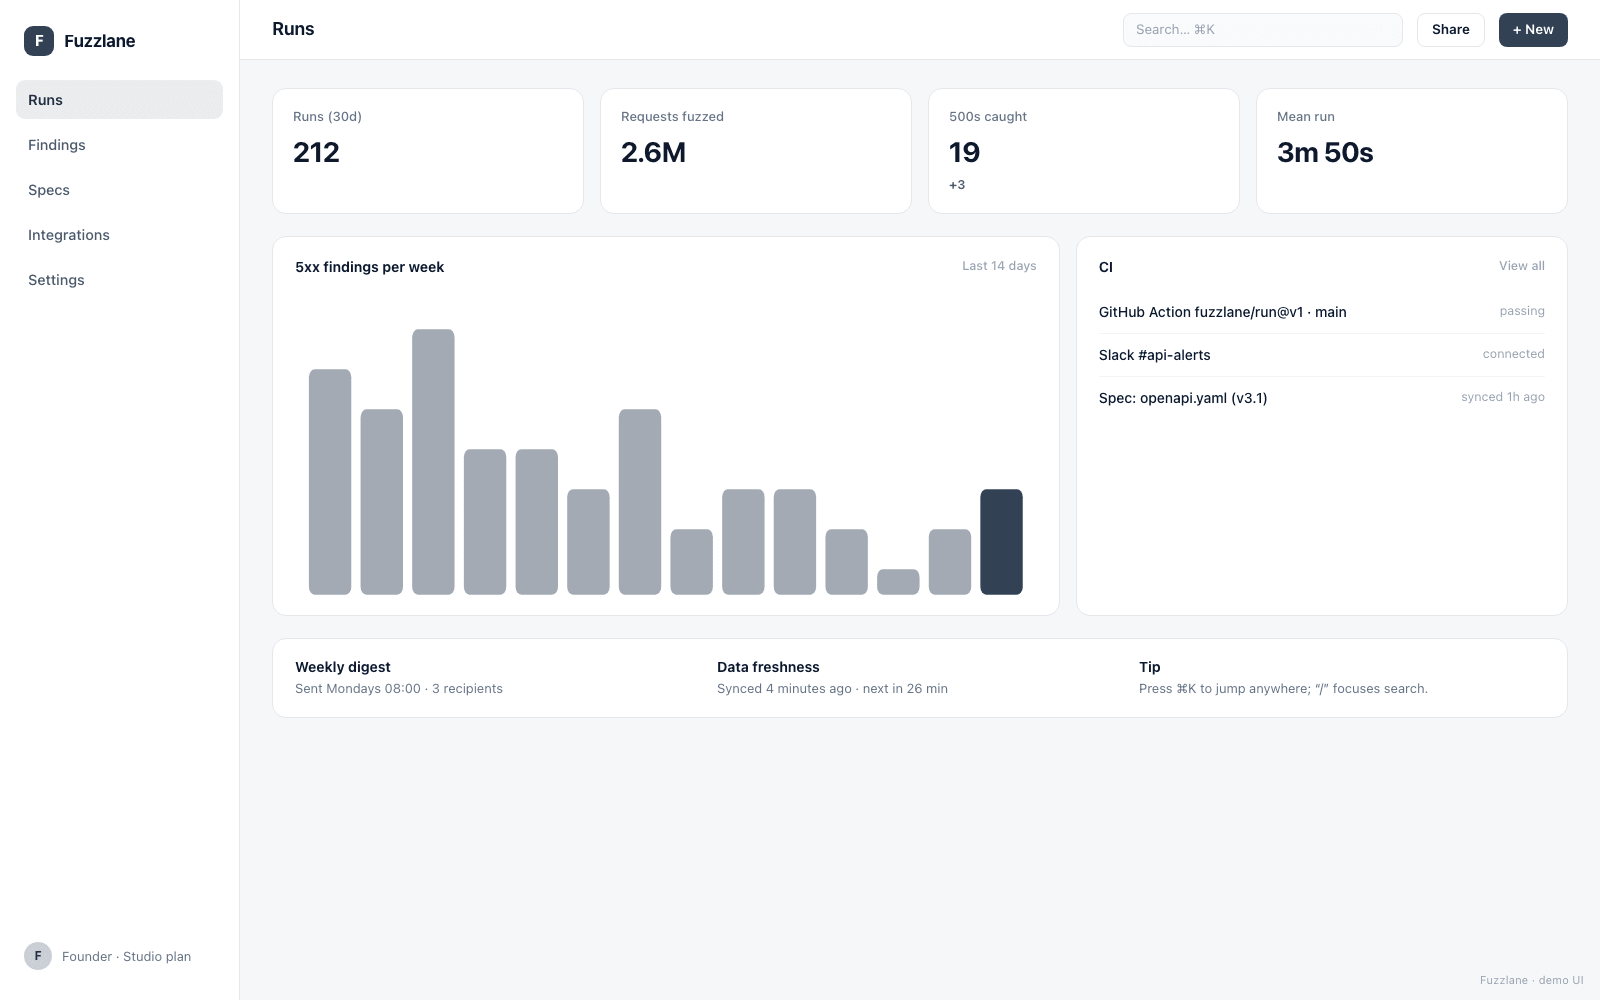
Point Fuzzlane at your OpenAPI spec and it generates and runs thousands of edge-case requests in CI — malformed payloads, boundary values, auth bypass attempts — and fails the build on 500s and leaks before a user or an attacker finds them.
securityopenapitesting
What the founder wants to know
“Pitch review: is this a product or a GitHub Action? Would you pay, and who in the org would?”